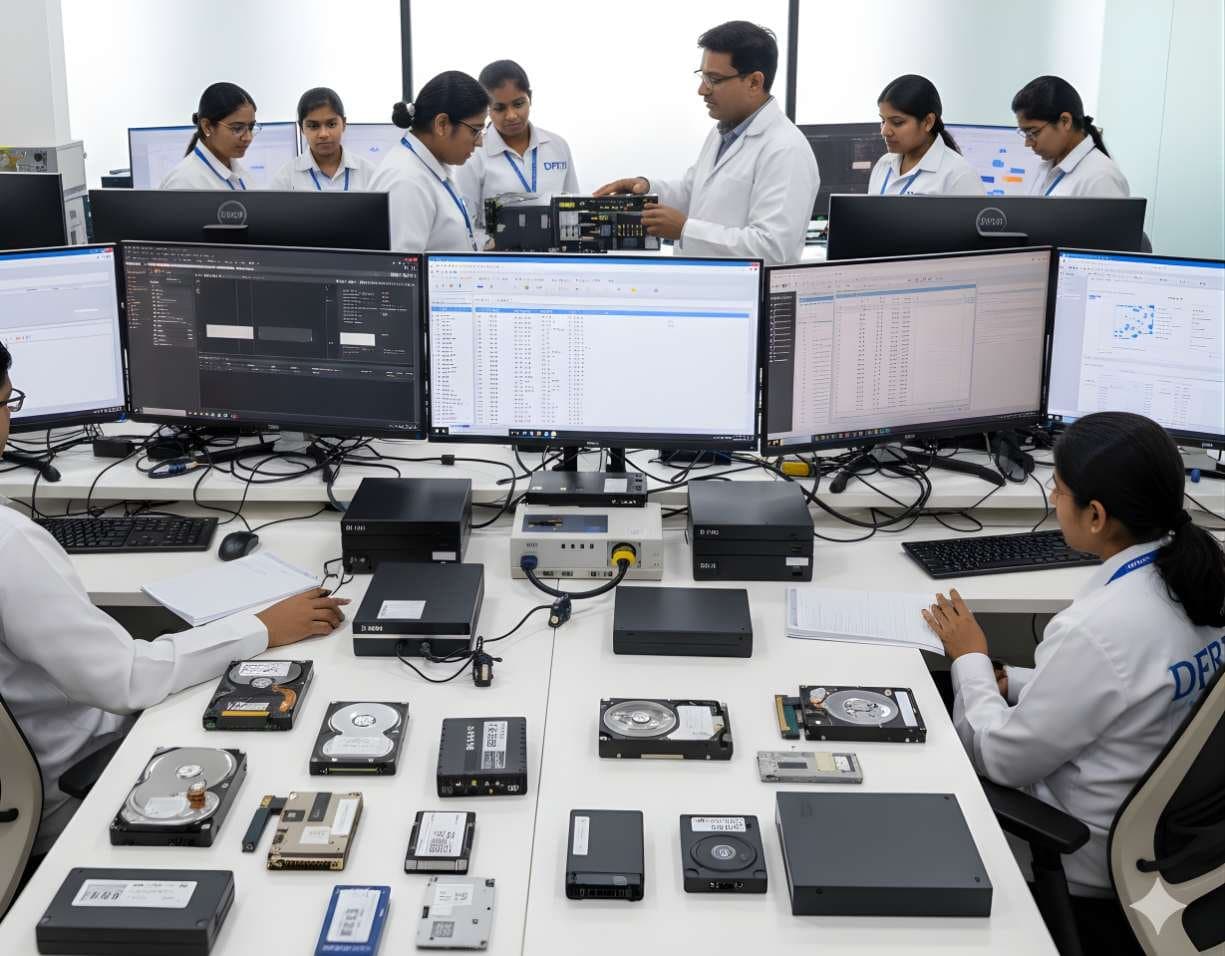
 StorageDigital Storage ForensicsHDD ForensicsImage hard drives through a write-blocker, find hidden areas and recover deleted data.
All courses
27 courses in seven tracks, from forensic basics and report writing to mobile, cloud, malware and AI forensics. Every course has lab work on real devices and evidence.
27 courses
StorageDigital Storage ForensicsHDD ForensicsImage hard drives through a write-blocker, find hidden areas and recover deleted data.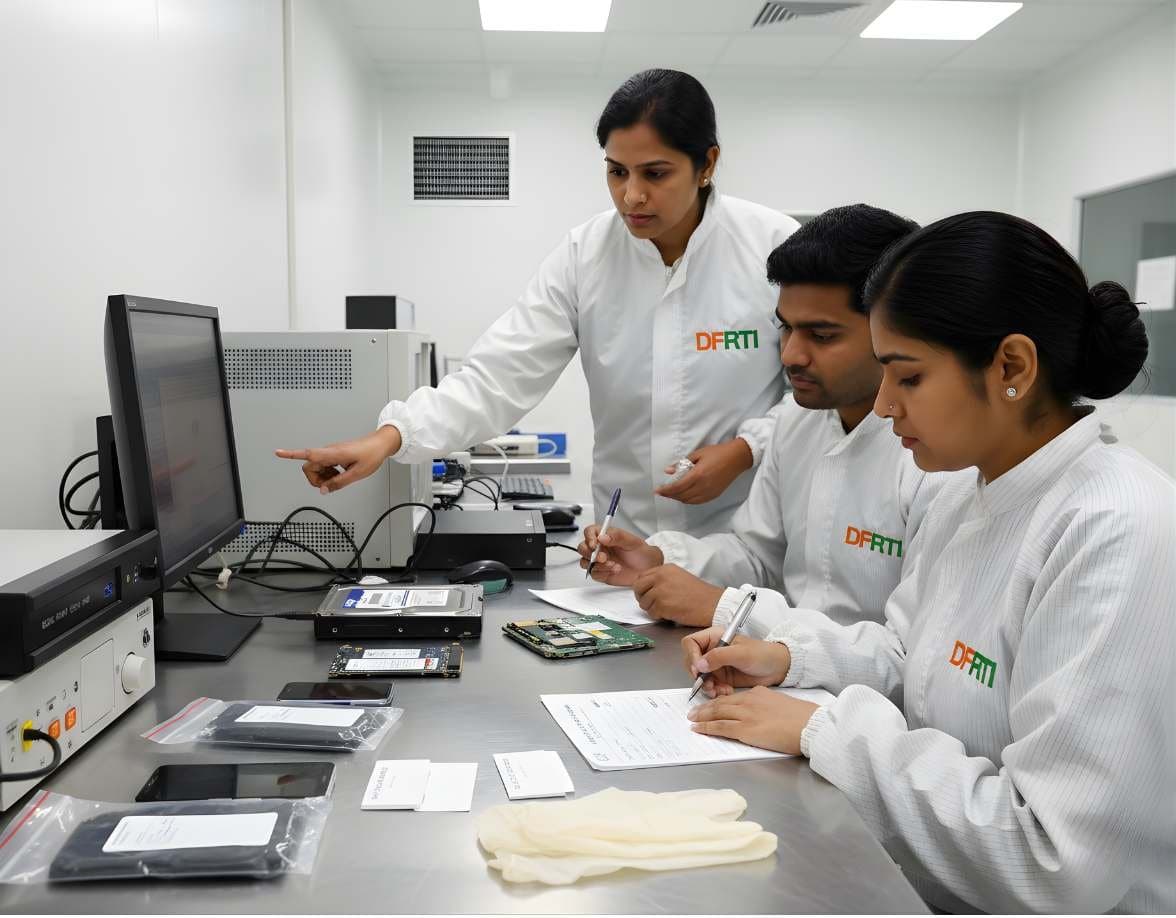 StorageDigital Storage ForensicsSSD / NVMe ForensicsHow TRIM, garbage collection and wear levelling change evidence on SSD and NVMe drives.
 StorageDigital Storage ForensicsUSB / Pen Drive ForensicsExamine pen drives and memory sticks and prove which USB device touched which computer.
 StorageDigital Storage ForensicsRAID / NAS ForensicsImage RAID members, rebuild arrays virtually and examine NAS boxes after ransomware.
 StorageDigital Storage ForensicsFile System AnalysisRead NTFS, FAT, exFAT, ext4 and APFS at the structure level and build timelines.
 MobileMobile & IoT ForensicsAndroid ForensicsExtract and examine Android phones, from ADB pulls to WhatsApp databases and ALEAPP reports
 MobileMobile & IoT ForensicsiOS ForensicsBFU and AFU states, iTunes and Finder backups, the keychain and iLEAPP for iPhone cases
 MobileMobile & IoT ForensicsSIM / Memory Card ForensicsICCID, IMSI and SMS from SIM cards, plus FAT and exFAT recovery from SD and microSD cards
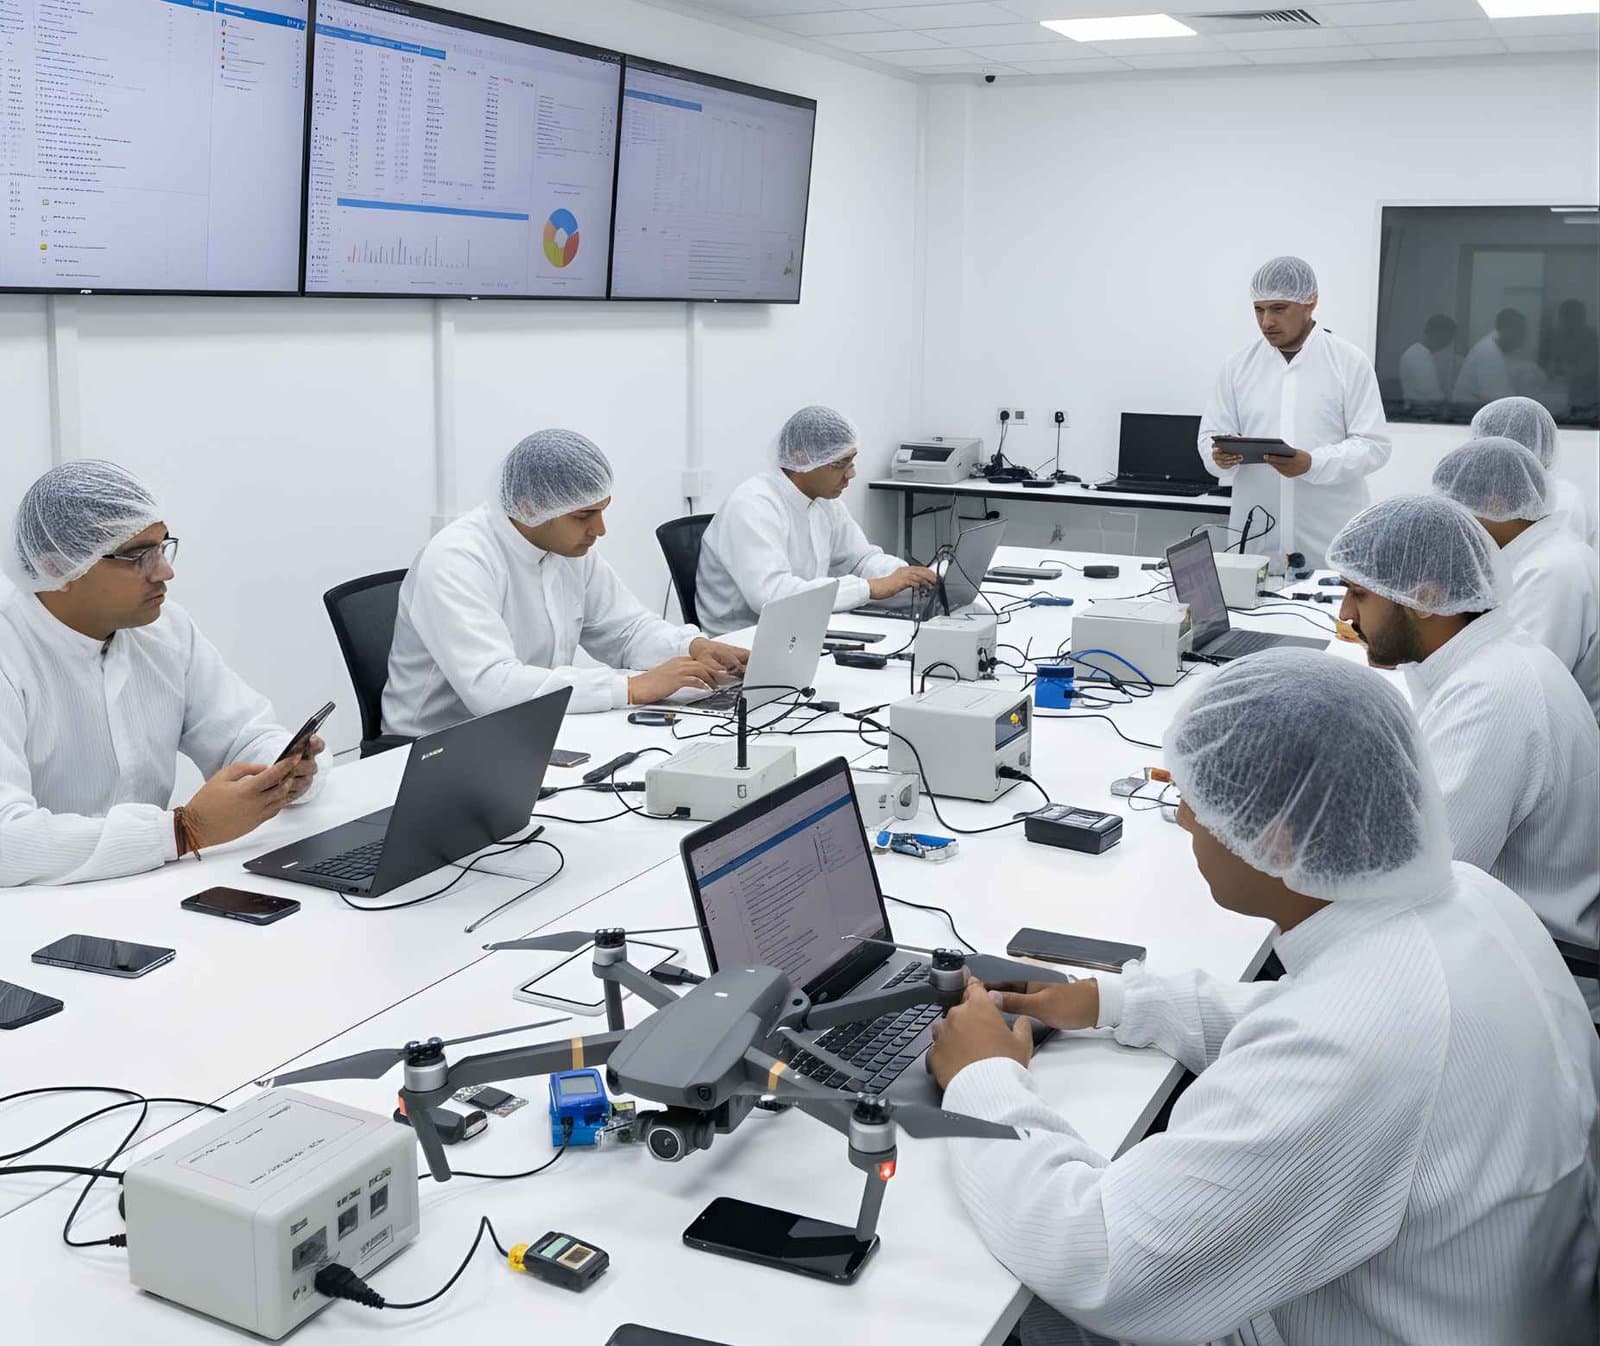 MobileMobile & IoT ForensicsDrone ForensicsRecover DJI flight logs, GPS tracks and home points from drones, controllers and phone apps
 MobileMobile & IoT ForensicsIoT Device ForensicsEvidence from smart speakers, cameras, wearables and routers, plus firmware extraction basics
 NetworkNetwork & Cloud ForensicsNetwork Traffic AnalysisRead flows, logs and packets to trace intrusions, beaconing and data theft.
 NetworkNetwork & Cloud ForensicsWireshark / Packet CaptureCapture, filter and read packets in Wireshark and tshark to recover what was sent.
 NetworkNetwork & Cloud ForensicsCloud Storage InvestigationCollect and read AWS, Microsoft 365 and Google Workspace logs as sound evidence.
 NetworkNetwork & Cloud ForensicsVirtual Machine / Hypervisor ForensicsExamine VMDK, VHDX and QCOW2 disks, snapshots, ESXi logs and VM memory files.
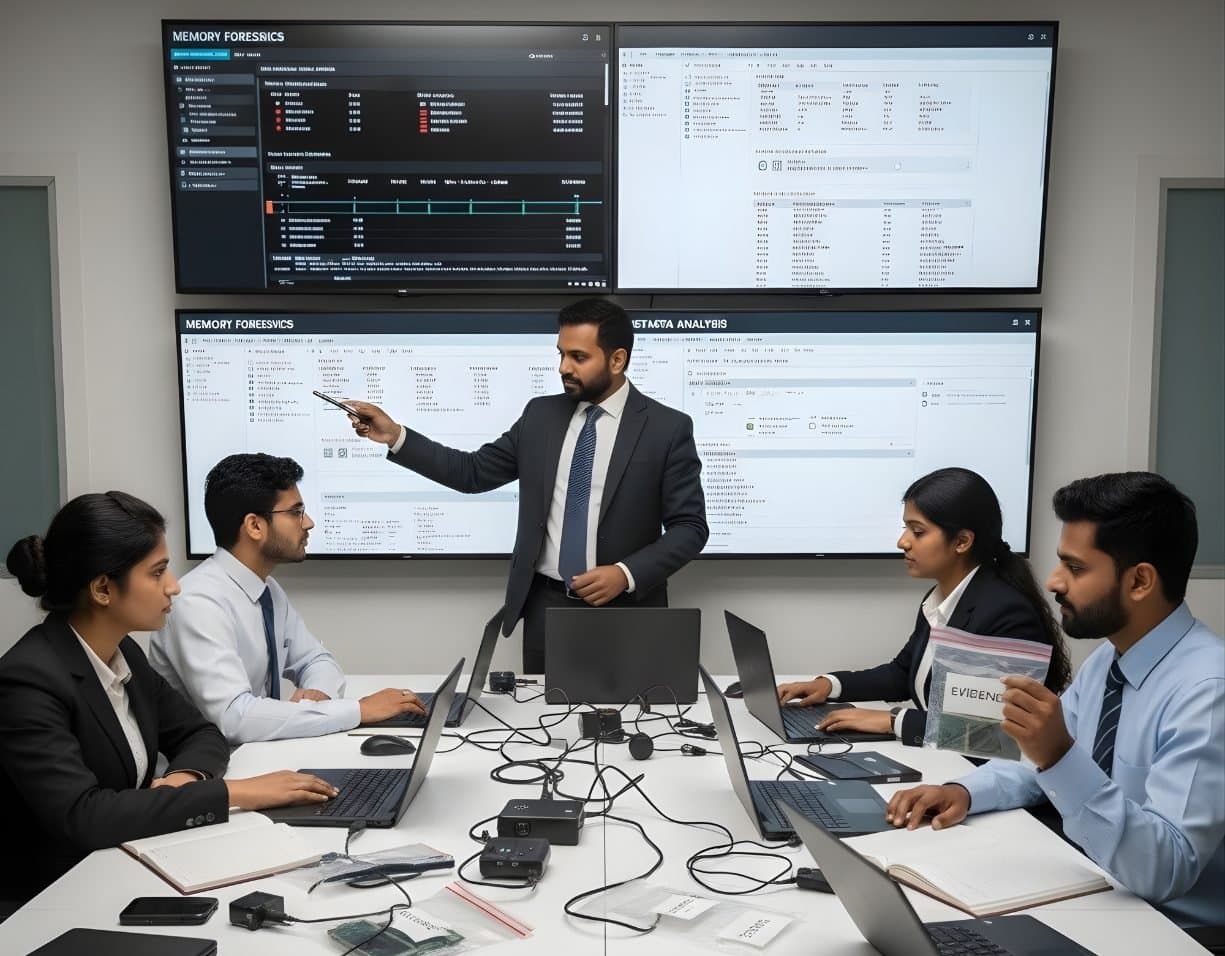 MalwareIncident Response & Malware AnalysisMemory ForensicsCapture RAM and use Volatility 3 to find hidden processes, injected code and connections.
 MalwareIncident Response & Malware AnalysisMalware Reverse EngineeringTake malware apart safely with static and dynamic analysis, Ghidra, x64dbg and YARA.
 MalwareIncident Response & Malware AnalysisRansomware & Threat ResponseHandle a ransomware attack from first call to recovery, reporting and lessons learnt.
 VideoSurveillance & Image / Video ForensicsCCTV / DVR AnalysisExport footage from Hikvision, Dahua and other DVRs with correct times, frames and hashes
 VideoSurveillance & Image / Video ForensicsImage & Video MetadataRead EXIF, XMP, GPS tags and MP4 atoms with ExifTool and know what each field can prove
 VideoSurveillance & Image / Video ForensicsDeepfake / AI ForensicsExamine face swaps and AI-made media, check C2PA provenance and know where detectors failAdvancedAdvanced & Specialised ForensicsAutomotive / Vehicle ForensicsRecover paired phones, trip logs and events from infotainment and telematics units
 AdvancedAdvanced & Specialised ForensicsCryptocurrency / Blockchain ForensicsTrace bitcoin and USDT flows, group wallets and prepare requests to exchanges
 AdvancedAdvanced & Specialised ForensicsAI / Machine Learning ForensicsUse machine learning to sort large evidence sets and investigate AI systemsAdvancedAdvanced & Specialised ForensicsOSINT / Open Source IntelligenceFind, verify and record public online information in a form a court can check
 LegalFoundation & Legal CoursesBasics of Cyber ForensicsStart here. Evidence handling, imaging, hashing, chain of custody and your first analysis.
 LegalFoundation & Legal CoursesForensic Report WritingWrite clear forensic reports that answer the questions asked and survive cross-examination.
 LegalFoundation & Legal CoursesLegal & Court ProceduresIndian law on electronic evidence: BSA Section 63, BNSS search and seizure and the IT Act.
Browse by track
 Digital Storage Forensics5 courses · HDD, SSD, file systems and data recovery
 Mobile & IoT Forensics5 courses · Android, iOS, SIM cards and IoT devices
 Network & Cloud Forensics4 courses · Traffic, logs, cloud accounts and virtual environments
 Incident Response & Malware Analysis3 courses · Malware analysis, memory forensics and threat investigation
 Surveillance & Image / Video Forensics3 courses · CCTV and DVR footage, metadata and deepfake detection
 Advanced & Specialised Forensics4 courses · Crypto wallet tracing, AI forensics, OSINT and drones
 Foundation & Legal Courses3 courses · Forensic principles, chain of custody and court procedure
Not sure this is the right one for you?
Tell us your background and what you want to do next. A counsellor will suggest a course and the next batch.